Lesson 3 of 14 · about 55 minutes · Updated November 15, 2026
Metrics and Reporting to Leadership
You'll be able to
- Distinguish activity, coverage, performance (KPI), risk (KRI) and impact metrics, and decide which belong in a board report.
- Apply NIST SP 800-55 Vol. 1 and Vol. 2 (December 2024) and CSF 2.0 profiles, tiers and Govern outcomes to build a measurement program.
- Define repeatable metrics for patch latency against known exploited vulnerabilities, MFA coverage, detection and response time, phishing reporting, vendor coverage, backup restores and privileged accounts, and recognize how each can mislead.
- Design a one-page board report and dashboard with targets, tolerances and trends, and prepare for the questions audit committees ask.
- Read 10-K Item 1C disclosures and recent director surveys critically, and avoid common benchmarking errors.
- Explain, from enforcement orders, how reporting systems fail when security facts do not reach decision makers.
Start here: the short version
- Most security reports measure effort, not risk. Counts of blocked attacks, scans run and tickets closed show that people are busy. A board needs a small set of numbers that show whether the chance and cost of a damaging incident are going up or down, compared with a target the board agreed to.
- NIST rewrote its measurement guide in December 2024. SP 800-55 now comes in two volumes: Volume 1 on choosing measures (implementation, effectiveness, efficiency and impact) and Volume 2 on running a measurement program. Its advice for new programs is blunt: with quantitative metrics, "less is often more."12
- The best operational metrics are tied to how real attacks happen: how fast internet-facing systems get fixed when a flaw is on CISA's Known Exploited Vulnerabilities list, how many accounts still lack phishing-resistant sign-in, how fast intrusions are found and contained, how often people report suspicious email, whether backups actually restore, and how many people hold administrator power.34
- Directors say they understand cyber, and also say they want better metrics. In NACD's 2025 survey of public company directors, about three in four agreed their board understood cybersecurity well enough to oversee it, yet "acquiring metrics to accurately measure and assess cybersecurity" drew the most "extremely important" votes of any improvement area.56
- Public companies now describe board reporting in their annual reports. Regulation S-K Item 106 requires a 10-K to say how the board is informed about cyber risk. Boise's Micron, IDACORP and Albertsons each describe quarterly or more frequent briefings, and one names "key information security risk metrics" as part of them.78910
- Enforcement cases keep finding the same failure: the facts were known somewhere in the company but never reached the people deciding. Capital One (2020), First American (2021), Blackbaud (2023) and R.R. Donnelley (2024) all turned on information that did not travel up.11121314
- A one-page report beats a forty-slide deck. This lesson ends with a sample Board Security Report template you can adapt.
Rules, standards and reports described: NIST SP 800-55 Vol. 1 and Vol. 2, Measurement Guide for Information Security (both published Dec. 4, 2024, replacing SP 800-55 Rev. 1 of July 2008); NIST Cybersecurity Framework 2.0 (CSWP 29, Feb. 26, 2024); SEC Regulation S-K Item 106 (17 CFR 229.106), adopted in Release 33-11216 (Aug. 4, 2023) and unchanged as of Nov. 15, 2026; FTC Safeguards Rule, 16 CFR 314.4 (eCFR current as of Nov. 2026); 23 NYCRR Part 500 as amended effective Nov. 1, 2023; 12 CFR Part 30, Appendix B; CISA Binding Operational Directive 26-04 (June 10, 2026), which revoked BOD 22-01; CISA Known Exploited Vulnerabilities catalog version 2026.11.13; FY 2025 IG FISMA Reporting Metrics, Version 2.0 (April 3, 2025), still in effect for FY 2026; NACD 2025 Public Company Board Practices and Oversight Survey (July 2025); Idaho Executive Order 2017-02 and Idaho Code 67-827 and 67-831 to 67-833. All read Nov. 15, 2026 unless a note says otherwise. Rules, survey results and agency directives change; check the current text before relying on any point.
Before you change anything. Plan changes to production systems, test them first, keep a way back, and follow your change management process. For clinical, plant-floor or other safety systems, involve the vendor, your safety lead and qualified engineers (see modules 109 and 111).
Picture the third quarter's audit committee meeting at a large regional hospital system. The chief information security officer has twelve minutes on the agenda, after the external auditor and before the pension report. The pre-read is a 38-slide deck. Slide 4 says the security operations center "processed 1.7 billion events and blocked 412,000 threats." Slide 11 is a heat map with nine red squares and no explanation of what would turn one green. Slide 23 says 96 percent of employees completed annual training. A director who used to run a manufacturing plant asks the only question that matters: "Are we safer than we were a year ago, and how would we know?" Nobody in the room can answer from the deck.
This lesson is about answering that question. It explains the kinds of security metrics, what the National Institute of Standards and Technology (NIST) now recommends, how to use the Cybersecurity Framework's profiles and tiers to show progress, which operational numbers actually track risk and which ones mislead, how to build a dashboard and a one-page board report, what audit committees ask, what public companies now say in their annual reports about board reporting, what research from 2024 to 2026 shows about how well boards understand what they are told, and where benchmarking goes wrong. It is written for directors, audit committee members, executives, CISOs and their staff, internal auditors, risk managers, public officials, and the reporters and advocates who read what these organizations publish.
It builds on two earlier lessons and does not repeat them. The legal duties behind board reporting (Caremark, the SEC rules, NYDFS Part 500, the FTC Safeguards Rule and the bank guidelines) are in Governance, Boards, Officers and Disclosure, which also has a short list of board metrics this lesson expands. Smaller-scale board reporting is in Privacy Program, AI Governance and Board Reporting. Risk registers, risk appetite and dollar-based risk analysis (FAIR) are in Risk Management in Plain Terms. Inside this module, the program that produces these numbers is described in Building the Security Program, the budget the numbers are used to defend is in Budgets, Staffing and the Business Case, internal audit's independent check on the numbers is in Internal Audit, SOX and the Three Lines, and maturity scoring is in Program Maturity Checklist and Roadmap.
What a security metric is
People use "measure," "metric," "indicator" and "KPI" loosely. NIST's 2024 guide draws useful lines between them, and the distinctions matter when a board asks where a number came from.
- Measurement is "the process of obtaining quantitative values using quantitative methods."1
- Measures are "quantifiable and objective values that result from measurement," for example the number of servers missing a patch on a given date.1
- Metrics are "measures and assessment results designed to track progress, facilitate decision-making, and improve performance with respect to a set target."1 The phrase "with respect to a set target" is the heart of it. A number without a target is a measure; it becomes a metric when someone has decided what good looks like.
- Assessment results can be qualitative (high, medium, low), semi-quantitative (scores on a 1 to 5 scale whose numbers mean nothing outside that scale) or quantitative (numbers that keep their meaning anywhere, such as days or dollars). NIST says qualitative and semi-quantitative results are not measurements in its sense, though they may still be useful.1
The last point is the one boards most often miss. A heat map that rates ransomware risk "4 out of 5" is a semi-quantitative judgment. It can be useful for sorting a risk register, but a 4 is not twice as bad as a 2, and two 4s from two different business units may not mean the same thing. When a board is shown a trend in heat map colors, it is seeing a trend in someone's opinion. That is not wrong, but it should be labeled as opinion and backed by measures where possible.
NIST also notes that metrics work at three levels. System-level metrics, such as "the frequency of third-party access to a system or the number of communication ports open," support day-to-day decisions. Program-level metrics, such as "the number of security incidents in a year or the cost per incident," support strategy. Organization-level metrics roll the two up for the people who set risk appetite.1 A board report should almost never contain a system-level metric unless that one system is the risk.
Activity, performance and risk metrics
A practical way to sort the hundreds of numbers a security program can produce is by the question each one answers.
| Kind of metric | Question it answers | Examples | Who should see it |
|---|---|---|---|
| Activity (operational counts) | How busy were we? | Alerts processed, emails blocked, scans run, tickets closed, training modules assigned. | Team leads managing workload. Rarely executives; almost never the board. |
| Coverage or implementation | Is the control in place where it should be? | Percent of laptops and servers with endpoint detection; percent of accounts with phishing-resistant multifactor authentication (MFA); percent of critical systems sending logs. | Program managers and executives; the board sees the few that matter most. |
| Performance (effectiveness and efficiency), usually called key performance indicators or KPIs | Is the control working, and how fast? | Median days to fix known exploited flaws on internet-facing systems; mean time to detect and to contain; percent of backup restore tests that succeed. | Executives and the board committee, with a target and a trend. |
| Risk, usually called key risk indicators or KRIs | Is a specific risk growing past what we said we would accept? | Count of internet-facing systems with a known exploited flaw past its deadline; number of critical vendors with no current assessment; open high-risk policy exceptions older than 90 days. | The board and its committee, against a tolerance the board approved. |
| Impact | What did security cost or save the mission? | Loss events and their cost; downtime of critical services; regulatory penalties; insurance claims paid. | The board and the CFO. |
The difference between a KPI and a KRI is direction. A KPI tells you how well a process performs; a KRI warns that exposure is rising. The same raw data can feed both. "Median days to patch" is a KPI. "Number of internet-facing systems with a known exploited flaw unpatched past 14 days" is a KRI, because each one is an open door, and the board can set a tolerance (for example, zero for more than seven days running) and expect to be told when it is breached. NIST calls KRIs and KPIs "examples of metrics, though not all metrics fall into these categories."1 Some programs also track key control indicators, which test whether a single control is operating (for example, whether privileged access reviews happened on schedule).
A second useful split is leading versus lagging. Lagging indicators count what already happened: incidents, losses, audit findings. Leading indicators measure conditions that make future incidents more or less likely: unpatched exposure, accounts without MFA, untested backups. Boards tend to receive lagging indicators because they are easy to count. The lagging numbers in security are also small and noisy (a large company may have one material incident in five years), so a quarter with no incidents says little. A good report pairs a few lagging numbers with leading ones that explain why the next quarter is likely to be better or worse.
NIST SP 800-55: the measurement guide
For sixteen years the standard federal reference on security metrics was NIST SP 800-55 Revision 1, Performance Measurement Guide for Information Security, from July 2008. NIST released drafts of a second revision in 2024 under the working name "Rev. 2," then published the final text on Dec. 4, 2024 as two volumes with new names: SP 800-55 Vol. 1, Identifying and Selecting Measures, and SP 800-55 Vol. 2, Developing an Information Security Measurement Program, both by Katherine Schroeder, Hung Trinh and Victoria Pillitteri. Volume 1 formally supersedes the 2008 revision.12 Anyone citing "SP 800-55 Rev. 2" in a policy or a request for proposals is citing the draft name; the final documents are Vol. 1 and Vol. 2. Both are free.
Volume 1: four types of measures
Volume 1 sorts measures into four types, which line up closely with the pyramid above:1
- Implementation measures "demonstrate the progress of specific controls," usually as percentages, for example "the percentage of systems with approved system security plans." NIST notes that organizations "never fully retire implementation measures because they are a record of what exists and what needs improvement."
- Effectiveness measures "evaluate how well implementation processes and controls are working and whether they are meeting desired outcomes."
- Efficiency measures "examine the timeliness of controls by determining the speed at which they give useful feedback and how quickly those issues are addressed." NIST groups effectiveness and efficiency together as "Program Results."
- Impact measures express "the impact of information security on an organization's unique mission," including cost savings, the costs of handling events, regulatory fines, contractual penalties and "the degree of public trust gained or maintained." NIST says these "are sought by executives" and that they need further analysis "before the results can be expressed to a non-technical audience."
The guide also sets out qualities of a good metric: it should be "objective, accurate, precise, tied to a fixed reference or point in time, replicable, and comparable to previous measurements." And it gives a warning that every CISO building a first dashboard should read: "Poorly selected quantitative metrics can undermine the overall quality of reporting and erode confidence in the work product. ... With quantitative metrics - initially at least - less is often more."1 The test it proposes is whether "the data point directly illustrates the performance of a valid control or tracks the presence of a material risk to the organization's objective. If not, it may be best to exclude the data item."
Volume 1 also recommends keeping metrics stable so trends mean something: tracking the same measure "over a continuous period (e.g., quarter to quarter, year to year) will give more information" than adding new ones every cycle.1 It gives a small example that applies to every awareness program: when evaluating training, "consider completion rates and the results of review quizzes instead of marking participation as 'low, medium, or high.'"
Volume 2: running a measurement program
Volume 2 describes the workflow for a measurement program in five activities: evaluating and defining the existing security program; identifying and prioritizing measures; collecting and analyzing data; identifying corrective actions; and applying corrective actions. NIST presents them in order but says the work is iterative.2 Data collection includes rolling system-level measures up into program-level ones, storing the data in a form that can be analyzed, and running a gap analysis "to compare the collected measurements with targets (if defined)."
Two points from Volume 2 are worth repeating to executives. First, a single bad number rarely explains itself. NIST's example: finding that the percentage of approved system security plans is "unacceptably low would not correct the problem"; the organization has to find the reasons, such as "lack of guidelines, insufficient expertise, or conflicting priorities," and aim the fix at the cause.2 Second, measurement programs mature. Early on, the focus is on whether controls exist ("implementation, coverage, functionality, or capability"); as those goals are met, "the emphasis on measurement can be migrated toward efficiency, effectiveness, and business impacts."2 A board that demands dollar-denominated risk figures from a program that cannot yet say how many servers it owns is asking for numbers that will be invented.
Volume 2 also assigns measurement duties by role. For the chief executive or agency head, these include "ensuring that information security measures are used in support of strategic and operational planning," "providing adequate financial and human resources for successful information security measurement activities," and "approving policies to officially institute measures collection." For the chief information officer, they include using measures "to report on the effectiveness of the organization's information security program" and making sure there is a process "to prioritize and address issues discovered through measures analysis."2 Measurement, in other words, is a management duty, not a hobby of the security team.
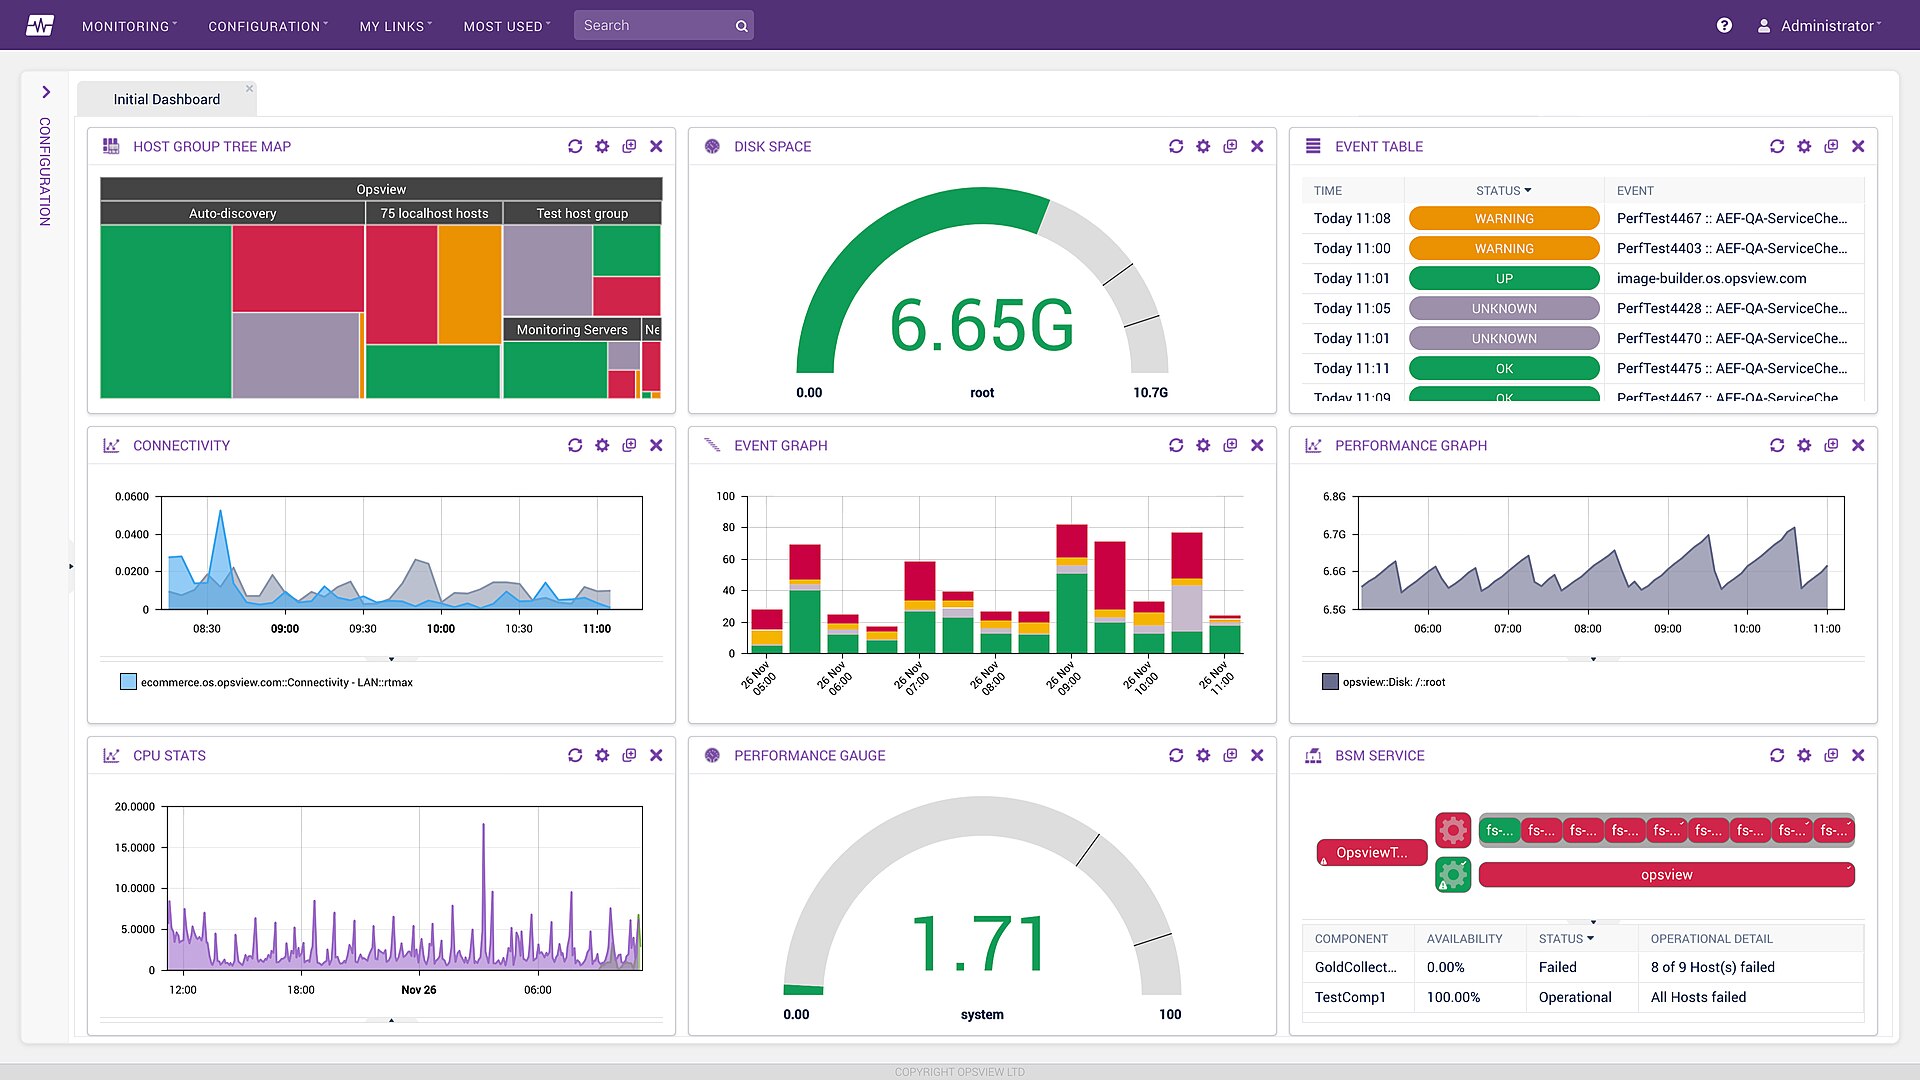

CSF 2.0 profiles and tiers as a measurement tool
The NIST Cybersecurity Framework (CSF) 2.0, published Feb. 26, 2024, is not a metrics standard, but two of its parts are among the most useful reporting tools a large organization has. The Standards Map explains the framework's six functions and how it maps to other standards; this section covers only how to use it to measure and report.
Current and target profiles
A CSF Organizational Profile describes an organization's security posture in terms of the framework's outcomes. NIST defines two kinds. A Current Profile "specifies the Core outcomes that an organization is currently achieving (or attempting to achieve) and characterizes how or to what extent each outcome is being achieved." A Target Profile "specifies the desired outcomes that an organization has selected and prioritized for achieving its cybersecurity risk management objectives."15 NIST lays out five steps: scope the profile, gather information, create it, "analyze the gaps between the Current and Target Profiles, and create an action plan," and then implement the plan and update the profile.15 The action plan can be a risk register or a "Plan of Action and Milestones [POA&M]," the federal term for a dated list of fixes.
For reporting, this gives the board something better than a single maturity score: a short list of outcomes the organization chose to improve, where it stands on each, and the dated plan to close each gap. A useful board view shows perhaps eight to twelve priority outcomes from the Target Profile, the current state of each, the owner, and the quarter in which the gap is due to close. Progress against that list is a measure of management performance, not of the security team's activity.
NIST also notes that a profile can be scoped narrowly, for example "to an organization's financial systems or to countering ransomware threats." A board that is most worried about ransomware can ask for a ransomware-scoped profile and track it separately.15
Tiers are not a maturity score
CSF 2.0 has four Tiers: Partial (Tier 1), Risk Informed (Tier 2), Repeatable (Tier 3) and Adaptive (Tier 4). NIST says they "characterize the rigor of an organization's cybersecurity risk governance and management practices" and "describe a progression from informal, ad hoc responses to approaches that are agile, risk-informed, and continuously improving."15 Organizations may use them to inform their Current and Target Profiles.
Tiers are often presented to boards as a maturity scale ("we are a 2.6 moving to a 3.2"). Two cautions apply. First, the Tiers are four broad descriptions, so any decimal score is the organization's own invention, a semi-quantitative judgment in NIST's terms. Second, not every organization should aim for Tier 4 everywhere; NIST frames tier selection as setting "the overall tone for how an organization will manage its cybersecurity risks," which is a risk and cost decision.15 A tier score is a reasonable way to summarize governance rigor once a year; it is a poor way to show quarter-to-quarter progress. Maturity models in general are compared in lesson 14.
The Govern function asks for measurement
CSF 2.0 builds measurement into governance. Under the Oversight category, "Results of organization-wide cybersecurity risk management activities and performance are used to inform, improve, and adjust the risk management strategy," with outcome GV.OV-03: "Organizational cybersecurity risk management performance is evaluated and reviewed for adjustments needed."15 Under Risk Management Strategy, GV.RM-02 calls for "risk appetite and risk tolerance statements" and GV.RM-06 for "a standardized method for calculating, documenting, categorizing, and prioritizing cybersecurity risks."15 Under Identify, the Improvement category expects improvements to come from evaluations, tests and exercises, and day-to-day operations (ID.IM-01 to ID.IM-03).15 Put together: the framework expects an organization to have a stated tolerance, to measure against it, and to show the board that the measurement changed decisions.
The federal version: FISMA maturity levels
Federal agencies have measured their programs this way for years under the Federal Information Security Modernization Act of 2014 (FISMA). Each year agency inspectors general rate their agency's program using metrics issued by the Office of Management and Budget (OMB), the Council of the Inspectors General on Integrity and Efficiency (CIGIE) and CISA. The FY 2025 IG FISMA Reporting Metrics (Version 2.0, April 3, 2025) organize the review by the six CSF 2.0 functions and rate each area on five maturity levels: Ad Hoc, Defined, Consistently Implemented, Managed and Measurable, and Optimized. OMB treats Level 4 as the line: "achieving a Level 4 (managed and measurable) or above represents an effective level of security."16 For FY 2026, CIGIE's own audited FISMA report states that the FY 2025 metrics "remained in effect."17
The federal model is worth knowing for two reasons outside government. First, the line between Level 3 and Level 4 is exactly the line this lesson is about: a control can be "consistently implemented" and still not be measured. Level 4 requires that effectiveness be measured and used to drive change. Second, inspector general FISMA reports are public, so anyone can read how an independent auditor describes the gap between an agency's policies and its measurements.
Metrics that track risk, and metrics that mislead
The operational metrics below are the ones most large programs settle on after a few years, because each one is tied to a way real breaches happen. For each, this section gives a definition precise enough to be repeatable, a reason it matters, and the ways it is commonly gamed or misread. The numbers in the examples are illustrative unless a source is cited.
Patch latency against known exploited vulnerability deadlines
What it measures. How long internet-facing and other high-value systems stay exposed to software flaws that attackers are already using. The usual reference list is CISA's Known Exploited Vulnerabilities (KEV) catalog, a free federal list of flaws with reliable evidence of active exploitation. Catalog version 2026.11.13, released Nov. 13, 2026, held 1,781 entries, 361 of them marked as known to be used in ransomware campaigns.3
Why it matters. Exploiting a vulnerability has become a leading way into organizations. Verizon's 2025 Data Breach Investigations Report found it was the first step in 20 percent of breaches, and that of the edge-device vulnerabilities organizations knew about, only about 54 percent were fully fixed during the year, at a median of 32 days.18 Verizon's 2026 report puts exploitation at 31 percent of breaches, ahead of stolen credentials.19 Published summaries of the full 2026 report put the median time to fix known exploited flaws at 43 days, with only 26 percent fully fixed; those two remediation figures come from a secondary summary and are treated as uncertain here.20 Mandiant's M-Trends 2026 found exploits were "the most common initial infection vector for the sixth consecutive year, accounting for 32% of intrusions" in its 2025 investigations.4
The federal deadlines changed in 2026. From November 2021 to June 2026, CISA's Binding Operational Directive 22-01 required federal civilian agencies to fix KEV-listed flaws by a due date in the catalog, generally two weeks for newer flaws. Many private organizations copied those due dates as their own targets, which made "percent of KEV items fixed by the CISA due date" a common board metric. On June 10, 2026, CISA revoked BOD 22-01 and replaced it with BOD 26-04, "Prioritizing Security Updates Based on Risk," which sets remediation clocks of 3, 14 or 60 days, or fix on the next system upgrade, depending on whether the flaw is in KEV, whether the system is exposed to the internet, whether exploitation can be automated, and how much control an attacker would gain. Agencies phase in the new timelines over 180 days.21 The KEV catalog itself continues. Organizations that tied their metric to the old KEV "due date" field should check whether their definitions still work and, if they adopt BOD 26-04's logic, restate past quarters on the new basis so the trend line is honest. Network and Cloud Security explains the directive in detail.
A good definition. "Number and percent of KEV-listed vulnerabilities on internet-facing assets that remained open past our internal deadline (3 days for exposed, automatable, high-impact flaws; 14 days otherwise) at quarter end, plus the age in days of the oldest open item." Report the count past deadline, not just the average. A median of 9 days can hide one firewall that has been exposed for 140 days, and that firewall is how the breach will happen.
How it misleads. The denominator only covers assets the scanner can see; unknown assets are invisible. Risk exceptions ("this system cannot be patched until the vendor certifies the fix") are sometimes removed from the count, which makes the number look better exactly where the risk is highest. Report exceptions as their own line, with compensating controls and an expiry date. When you change a system that runs production, plan the change, test it and have a way back; fast patching that breaks a hospital's scheduling system is not a success.
MFA coverage, and what kind of MFA
What it measures. The share of accounts that cannot be used with a stolen password alone. A useful version splits accounts into tiers: administrators and other privileged accounts; remote access and email for the whole workforce; customer-facing and third-party access; and service accounts that cannot use MFA at all.
Why it matters. Stolen or guessed credentials remain one of the most common ways in, and some forms of MFA (text message codes, push prompts that a tired user approves) can be defeated by phishing kits and by repeated prompting. Phishing-resistant methods, such as security keys and passkeys built on the FIDO standards, are much harder to defeat, which is why CISA and the federal zero trust strategy push them. Identity and Access covers the methods.
A good definition. "Percent of privileged accounts using phishing-resistant MFA; percent of all workforce accounts with any MFA on email, remote access and cloud consoles; count of accounts with MFA exempted, by reason and age." The exemption count is the KRI. Under the FTC Safeguards Rule, MFA is required "for any individual accessing any information system" unless the Qualified Individual approves an equivalent control in writing, so for financial institutions under that rule the exemption list is also a compliance record.22
How it misleads. "98 percent MFA coverage" usually means 98 percent of the accounts in the main identity system. The breach comes through the 2 percent, or through a legacy system, a vendor portal or a service account that was never in the denominator. Ask what is excluded.
Mean time to detect, contain and recover
What it measures. Mean time to detect (MTTD) is the time from the start of malicious activity to its discovery. Mean time to respond or contain (MTTR) runs from discovery to containment. Some programs add mean time to recover, from containment to normal operations.
Benchmarks, with care. Mandiant reported that the global median dwell time (start of intrusion to detection) in its 2025 investigations "rose to 14 days from 11 days," and that organizations first detected the intrusion themselves 52 percent of the time, up from 43 percent in 2024.4 IBM's Cost of a Data Breach Report 2025 put the mean time to identify and contain a breach at 241 days, "a 17-day reduction from the year prior," and said organizations that found breaches themselves saved about $900,000 compared with those whose breach was disclosed by the attacker.23 A secondary summary of IBM's 2026 report gives 247 days.24 The large gap between Mandiant's 14 days and IBM's 241 days is not a contradiction: they measure different intervals (dwell time versus the whole cycle to containment), use different samples (Mandiant's own incident response cases versus a survey of breached organizations), and report different statistics (median versus mean).
A good definition. Pick one clock and keep it. For example: "For each confirmed incident of severity 2 or higher, hours from earliest evidence of attacker activity (as later established by investigation) to first alert, and from first alert to containment; report the median and the longest case for the quarter, and the percent of incidents first detected internally." The share detected internally is often more stable and more telling than the time figures.
How it misleads. Most organizations have few serious incidents, so a mean over three incidents can swing wildly. The start time is often unknown until weeks later, so early figures get revised. And the measure only covers intrusions you found; the ones you missed have infinite dwell time and do not appear. Pair MTTD with measures of detection coverage (percent of critical systems sending logs; percent of endpoints with detection software reporting in the last 24 hours) and with the results of exercises that test detection on purpose, as described in lesson 7.
Phishing report rate, not just click rate
What it measures. How often employees report a suspicious message, both in simulations and for real.
Why the click rate alone misleads. Two large field studies found that common training formats barely changed click rates. A 15-month study of more than 14,000 employees at one company (Lain, Kostiainen and Capkun, 2022) found that people who received short "embedded" training after clicking were not less likely to click again, and an eight-month randomized study across more than 19,500 health system employees (Ho and colleagues, 2025) found that embedded training cut clicking by only about 2 percent.2526 Click rates also depend on how hard the test was. NIST's Phish Scale research showed that a simulated phish's difficulty, based on its warning cues and how well it fits the recipient's job, drives the click rate, so a program that switches to harder lures will see click rates rise even as people get better.27
What moves. Reporting. Verizon's 2025 report, using data from awareness vendors, found that employees who had training within the prior 30 days reported simulated phishing about 21 percent of the time, against a base rate of about 5 percent.28 Reports are also what security teams need: one early report of a real phishing campaign can let the team pull the message from every mailbox. A good definition: "Percent of simulated phishing messages reported within one hour; count of real phishing reports per month and median time from first delivery to first report; click rate shown only with the difficulty rating of the test." People, Training, Phishing and Insider Risk has the full discussion.
Third-party risk coverage
What it measures. Whether the vendors that could hurt the organization most have been assessed and are bound by contract to protect it. A workable set: percent of critical (tier 1) vendors with an assessment completed in the last 12 months; percent with contract terms on breach notice, audit rights and security requirements; count of critical vendors with open high-risk findings past their due date; and count of vendors whose products appeared on the KEV list this quarter.
Why it matters. Verizon's 2025 report found that breaches involving a third party doubled, from 15 to 30 percent.18 The 2024 Change Healthcare and CDK Global attacks showed how one supplier's outage can stop thousands of customers. Vendors and Supply Chain covers the program; SOC reports, one of its main evidence sources, are in lesson 5.
How it misleads. "100 percent of vendors assessed" can mean a questionnaire was emailed and returned unread. Measure the share of critical vendors where a finding led to a change (a contract term, a compensating control, a replacement), and the count of critical vendors nobody has tiered yet.
Backup restore success
What it measures. Whether the organization can actually get its critical systems and data back, in the time the business needs. Backup job success ("99.8 percent of nightly jobs completed") is an activity metric; it says nothing about whether a restore works.
A good definition. "For each tier 1 system, date of last full restore test from the protected (offline or immutable) copy; result; time to restore achieved versus the recovery time objective; percent of tier 1 systems tested in the last 12 months." Report failures plainly. A failed test found in a drill is a success of the testing program. Data Protection, Encryption, Retention and Backups covers the design, and lesson 12 covers recovery objectives and impact tolerances.
Privileged account counts
What it measures. How many people and machine accounts hold administrator power over critical systems, identity systems and cloud consoles, and whether that power is standing (always on) or granted just in time.
A good definition. "Number of standing domain or global administrator accounts (target: a small fixed number); number of privileged accounts not reviewed in the last quarter; percent of privileged sessions brokered through the privileged access tool; count of privileged accounts belonging to people who left or changed roles." A rising count of standing administrators is a leading indicator of a worse ransomware outcome, because attackers who reach one administrator account can usually reach everything.
Other metrics worth a place
- Asset inventory coverage: percent of devices and cloud accounts in the inventory with a named owner; count of unknown assets found by discovery scans. Everything else depends on this denominator.
- End-of-support systems: count of internet-facing devices and critical systems past the vendor's end of security support, with retirement dates. CISA's BOD 26-02 (Feb. 5, 2026) ordered federal agencies to remove unsupported edge devices on a schedule, which makes this a natural board KRI.29
- Policy exceptions and risk acceptances: open exceptions by severity and age, and how many have expired without renewal. This is where risk accumulates quietly. The process is in lesson 4.
- Overdue audit and test findings: count of high-risk findings from internal audit, regulators and penetration tests past their agreed fix date.
- Exercise results: date of the last executive tabletop that included the disclosure decision, and the number of improvement items still open from it.
Metrics to retire from board reports
Several popular numbers should stay in operational reports and out of the boardroom:
- "Attacks blocked." The number goes up when logging improves and down when a sensor breaks. It cannot be compared across companies, and it says nothing about the attack that was not blocked.
- Training completion rate alone. It measures compliance with the training policy, not behavior. Show it if a regulator requires the training, but pair it with reporting rates.
- Vulnerability totals. "We have 184,000 open vulnerabilities" alarms without informing. Most are low-risk; the few that matter are the ones attackers use on exposed systems.
- Single composite scores from a vendor or an internal formula, unless the board can see what is inside them and what would move them.
- Color without definition. A red, amber or green status with no stated threshold for each color invites optimism. Every color on a dashboard should map to a number.
Building the metric catalog
A large program usually keeps a written catalog of its metrics, one page or one database record per metric, so that the number means the same thing every quarter and an auditor can recompute it. NIST's Volume 2 describes this documentation as part of the measurement program, and internal audit will test it.2 A good catalog entry has these fields:
| Field | What to write | Example |
|---|---|---|
| Name and number | Short, stable name | KRI-03: Exposed known exploited vulnerabilities past deadline |
| Question it answers | The business question, in plain words | Are we leaving doors open that attackers are already using? |
| Type | Implementation, effectiveness, efficiency, impact; KPI or KRI | Efficiency; KRI |
| Formula | Exact numerator, denominator and exclusions | Count of KEV-listed CVEs on assets tagged internet-facing, open past internal deadline at 23:59 on the last day of the quarter; exceptions counted separately |
| Data source | System of record and how data is pulled | Vulnerability scanner export joined to asset inventory and KEV feed, automated weekly |
| Owner | The person accountable for the number moving | Vice president, infrastructure (not the CISO) |
| Target and tolerance | Goal, and the level that triggers escalation | Target 0; tolerance 3; above 3 for two weeks goes to the risk committee chair |
| Frequency | How often measured and reported | Measured weekly; reported monthly to executives, quarterly to the board |
| Known limits | What the number does not cover | Assets not in inventory; operational technology scanned only monthly |
| Change log | Date and reason for any definition change | Q3 2026: deadlines changed to follow BOD 26-04 tiers; prior quarters restated |
Three practices keep a catalog honest:
- Automate collection where possible. Hand-built spreadsheets invite errors and late-night edits before board meetings. NIST's Volume 2 expects that as programs mature, "measurement data collection becomes fully automated."2
- Give the owner of the number the power to move it. If the CISO owns a patching metric but the infrastructure team controls the maintenance windows, the metric measures the CISO's persuasiveness. Assign the metric to the executive who controls the outcome; the CISO reports it.
- Have the third line check it. Internal audit should periodically recompute a sample of board metrics from source data. The IIA's Cybersecurity Topical Requirement, effective Feb. 5, 2026, expects internal auditors to assess cyber governance, including how management reports to the board.30 Lesson 8 covers how that works.
A note on incentives: when a number becomes a target tied to someone's bonus, people find ways to hit the number without changing the risk. Economists call this Goodhart's law. Security examples include closing vulnerability tickets as "risk accepted" to meet a patch target, or excluding hard-to-patch systems from the scan scope. The defense is to pair every target metric with a second number that would reveal gaming (exceptions count, scan coverage) and to have someone independent look at both.

Reporting to the board
A board does not manage the security program; it oversees it. That changes what it needs to see. The 2026 fifth edition of the NACD and Internet Security Alliance Director's Handbook on Cyber-Risk Oversight, released April 16, 2026 with a foreword from CISA, makes "Guide cybersecurity risk measurement and reporting" one of its six principles.31 Translated into practice, a board report should let a director answer five questions in a few minutes:
- Where are we against the risk appetite we approved? The handful of KRIs with tolerances, and any breach of tolerance since the last meeting.
- Is it getting better or worse? Trends over at least four quarters, not a single snapshot.
- What happened? Significant incidents and near misses, at the organization and at critical vendors and peers, and what was learned.
- Are we doing what we said we would? Progress on the funded plan (the Target Profile gaps or roadmap), with dates slipped and why.
- What do you need from us? Decisions: risk acceptances above management's authority, budget, policy approvals, and anything the CISO believes the board should know that management disagrees with.
Everything else is an appendix.
The one-page report
Many boards now ask for a single page (or a single screen) as the cover of the cyber report, with detail behind it. The discipline of one page forces choices: the CISO must decide which six to ten numbers best describe the organization's top risks, and say in a sentence what each means. A workable layout:
- Top line: the overall assessment in one or two sentences, in plain English, including whether any tolerance was breached.
- Risk indicators: six to ten KRIs and KPIs, each with current value, target, tolerance, prior four quarters and a one-line explanation.
- Events: incidents of a defined severity, regulatory contacts, and notable incidents at peers or vendors that changed the risk picture.
- Plan: top initiatives with status against dates.
- Asks: decisions needed.
The sample template at the end of this lesson follows that layout.
Show the trend, and the tolerance
A single quarter's number invites the wrong question ("is 5 good?"). A trend against a tolerance line invites the right one ("why did it jump in the third quarter, and when will it come back under?"). Trend charts should use the same definition throughout; if the definition changes, show the break and restate earlier points where possible. Four to eight quarters is usually enough. Annotate the chart with the events that explain it: a new scanner that found more assets, an acquisition, a new federal directive.
Translating to business terms
Directors come from finance, operations, law and public service. They understand risk in terms of money, downtime, customers, regulators and reputation. Three translations help:
- Tie each KRI to a scenario on the risk register. "Exposed known exploited flaws" connects to "ransomware through an internet-facing device," which the register estimates in downtime and dollars. Risk Management in Plain Terms explains how to build those estimates, including the FAIR method for expressing risk as a range of probable annual loss.
- Use the organization's own units. A hospital thinks in diverted ambulances and canceled procedures; a bank in hours without payments; a county in days without property tax collection or 911 dispatch support.
- Give ranges, not false precision. "Our estimate of annual ransomware loss fell from a likely range of $8 million to $40 million to $5 million to $25 million after the backup project" is more honest than "risk reduced by 37.2 percent." NIST's Volume 1 notes that impact measures need analysis before they can be "expressed to a non-technical audience."1
Bad news has to travel up
The single most important property of a reporting system is that bad news reaches the people who can act on it, intact and fast. Every enforcement case in the common mistakes section below turned on the opposite. A reporting design that protects against it includes: a written escalation rule with thresholds (for example, any incident that may affect regulated data, any breach of a board tolerance, any regulator contact); a direct line from the CISO to the committee chair; a standing agenda item for "things we are worried about" that is not tied to a metric; and a record in the minutes of the questions directors asked and the follow-ups assigned. The Delaware SolarWinds derivative opinion described a board committee that did not report to the full board on cyber for 26 months and a full board that held no meetings or discussions on cybersecurity from the October 2018 IPO until the December 2020 attack; the court dismissed the case but called the reporting system "subpar."32 Minutes that show questions and follow-ups are a board's best evidence that it paid attention.
What audit committees ask
Audit committees oversee internal control, internal audit and disclosure, so their questions lean toward evidence and accountability. A director preparing for the cyber agenda item, or a CISO preparing to be asked, can expect versions of these:
- Which three risks worry you most, and what are the numbers that tell you whether each is getting better?
- Where did these numbers come from? Has anyone outside your team, such as internal audit, recomputed them?
- What changed in the definitions since last year, and did you restate the trend?
- What is excluded from each denominator: acquired companies, operational technology, cloud accounts, vendors?
- Which tolerances did we breach this year, how long did each breach last, and who decided what to do?
- What did the last penetration test, red team exercise or tabletop find that is still open?
- Which risks has management accepted rather than fixed, and which of those are above management's authority to accept?
- How would we know if an incident were material, and how fast would this committee hear about it? (The disclosure process is in Governance, Boards, Officers and Disclosure.)
- Do our 10-K statements about cyber oversight match what actually happens in this room?
- What would you tell us if your boss were not here?
The last question sounds pointed, but several boards make it routine by holding a short executive session with the CISO, without other managers present, once or twice a year, much as audit committees already do with the external auditor and the chief audit executive.
Regulatory minimums for board reporting
Some regulators set the floor for what the board must receive. In summary (full detail in Governance, Boards, Officers and Disclosure):
| Rule | Who it covers | What the board must receive |
|---|---|---|
| FTC Safeguards Rule, 16 CFR 314.4(i) | Non-bank financial institutions under FTC jurisdiction (mortgage brokers, auto dealers that finance, tax preparers, many fintechs) | A written report from the Qualified Individual "regularly and at least annually" on the program's overall status and compliance, and on material matters including risk assessment, risk management and control decisions, service provider arrangements, testing results, security events and management's responses, and recommended changes.22 |
| 23 NYCRR 500.4 | Banks, insurers and other entities licensed by the New York Department of Financial Services | A written CISO report at least annually on the program, material risks, overall effectiveness, material events and plans to fix material inadequacies, plus timely reports on material issues; the board must have "sufficient understanding" of cyber to oversee it.33 |
| 12 CFR Part 30, Appendix B, section III.F | National banks and federal savings associations (parallel rules for state banks and credit unions) | A report to the board or a committee at least annually on the program's status and material matters.34 |
| Regulation S-K Item 106(c) | SEC-registered public companies | No required content, but the 10-K must describe how the board or a committee "is informed about such risks" and whether management reports to the board.7 |
These are floors. None of them requires quarterly reporting, specific metrics or trends, but each requires a record, and a record that contains only an annual slide deck with activity counts is a weak one when a regulator or a plaintiff asks what the board knew.
What 10-K filings say about board reporting
Since fiscal years ending on or after Dec. 15, 2023, every SEC-registered company's annual report on Form 10-K has included Item 1C, Cybersecurity, which carries the disclosures required by Regulation S-K Item 106. Paragraph (c)(1) requires a description of "the board of directors' oversight of risks from cybersecurity threats," including, if applicable, the responsible committee and "the processes by which the board or such committee is informed about such risks." Paragraph (c)(2) asks for management's role, including the relevant expertise of the people responsible, "the processes by which such persons or committees are informed about and monitor the prevention, detection, mitigation, and remediation of cybersecurity incidents," and whether they report to the board.735 These sections are now the largest public record of how companies say their boards are briefed. Three Boise-based companies show the range.
Micron Technology (fiscal 2026 10-K, filed Oct. 9, 2026)
The memory chipmaker says its board oversees cyber risk "directly as a whole, as well as through the Audit Committee," which oversees "monitoring and incident response, risk mitigation, supply chain security, product security, insider trust, and other security-related items." Its Chief Security Officer and Chief Information Officer "provide quarterly briefings to the Audit Committee regarding our company's cybersecurity risks and activities, including any recent cybersecurity incidents and related responses, cybersecurity systems testing, activities of third parties, and the like," the committee gives "regular updates" to the full board, and the two officers brief the full board annually. The filing says the program is aligned with the NIST Cybersecurity Framework and that the company has not experienced any incidents "determined to be material."8
IDACORP and Idaho Power (2025 10-K, filed Feb. 19, 2026)
The parent of Idaho's largest electric utility says the board oversees cyber risk "through the audit committee and the executive committee." Management's information security activities include "briefing the audit committee and the board on information security matters several times a year in their regular meetings and on an ad hoc basis," an annual security training program and external security assessments. Day-to-day work is led by a cybersecurity manager who reports to Idaho Power's director of security, and the filing names standards from the Center for Internet Security and NIST as the basis of its framework.9 As a utility, Idaho Power is also subject to the North American Electric Reliability Corporation's mandatory Critical Infrastructure Protection standards for its bulk power systems, described in Sector Rules.
Albertsons Companies (fiscal 2025 10-K, filed April 27, 2026)
The grocery chain splits oversight between an Audit and Risk Committee, which "reviews and discusses with management cybersecurity risks," and a Technology Committee responsible for technology risk including cybersecurity. Internal audit reports quarterly to the Audit Committee on "its reviews of the Company's cybersecurity risk exposures, controls and management actions." The CISO "presents cybersecurity related topics quarterly to the Technology Committee, including reviews of key information security risk metrics and program maturity progress, and annually updates the Board on external assessments." The filing also says the company runs periodic NIST Cybersecurity Framework assessments "conducted by a third party," and it disclosed that a new CISO started April 26, 2026.10
What the filings show, and do not
Read side by side, the three filings show the common pattern: a named committee, a stated frequency (quarterly or "several times a year"), an annual full-board session, and a reference to NIST. Only Albertsons names metrics and maturity progress as part of the briefing, and only Albertsons describes internal audit reporting to the committee on cyber. Some very large companies put almost nothing in Item 1C itself: JPMorganChase's 2025 10-K Item 1C is a single sentence pointing readers to the operational risk section of its management's discussion and analysis.36 That is permitted, but it means a reader has to look elsewhere in the filing.
What none of these filings contains is the metrics themselves. Item 106 does not require them, and companies have reason not to publish numbers that could help attackers or support a lawsuit. A reader can learn who is briefed and how often, but not whether the briefings contain bad news. That is why the SEC's enforcement cases, discussed below, focus on whether information actually reached the people making disclosures.
What boards understand: research from 2024 to 2026
Several recent surveys ask directors how well they understand cyber risk and how good their reporting is. All of them are self-reports from people with a reason to rate themselves well, so they show perception, not competence. Still, the patterns are consistent.
- Directors are confident. In the National Association of Corporate Directors' 2025 Public Company Board Practices and Oversight Survey (data released July 2025), 73.13 percent of responding directors agreed (47.50 percent somewhat, 25.63 percent strongly) that "my own understanding of cybersecurity is strong enough to provide effective oversight," and 75.01 percent agreed their board's collective understanding was. 78.75 percent said their board's understanding had significantly improved compared with two years earlier, and 85.00 percent were confident the organization could "effectively respond to a materially significant cyber incident." Only 27.22 percent agreed the board would benefit from recruiting a director with cyber expertise. These items had 158 to 160 respondents.5
- But they want better numbers. Asked how important it was for their board to improve in eight areas of cyber oversight, the item with the highest share of "extremely important" answers was "acquiring metrics to accurately measure and assess cybersecurity" (12.66 percent extremely, 33.54 percent very important, 158 respondents). "Quality of management reporting" was rated very or extremely important by 43.04 percent.6
- Fewer boards test themselves. In the same survey, 73.46 percent of boards had reviewed the most significant cyber threats in the past year and 70.99 percent had reviewed the breach response plan, but only 32.72 percent had participated in a test of the response plan, and only 29.01 percent had assigned clearly defined cyber oversight roles to the full board (162 respondents).37
- Directors grade CISO reporting as mixed. A 2026 CISO-Board Engagement report by IANS Research, Artico Search and The CAP Group, released March 24, 2026, found that 29 percent of directors rated cyber updates "very effective," 53 percent somewhat effective and 18 percent neutral. Reporting on regulatory trends scored best; reporting on the impact of evolving threats scored worst, with 53 percent of directors saying it needed improvement, and 41 percent said the same of the "cyber business risk assessment." The published summary does not give the sample size.38
The fair reading: boards believe they understand cyber better than they did, and they probably do, but the area they most want improved is measurement, and the reporting they rate lowest is the part that connects threats to business risk. That is the gap this lesson is about. The confidence numbers also deserve a skeptical look; only about a third of boards had practiced a response, so their confidence in responding to a major incident is largely untested.
Benchmarking pitfalls
Boards naturally ask, "How do we compare?" Benchmarks can help, but security benchmarks are unusually easy to misuse.
- Different definitions. "Mean time to respond" at one company starts at the first alert; at another, at the moment a human opens the ticket. "Critical vendor" may mean 40 suppliers at one bank and 400 at another. Comparisons of numbers with different definitions are noise.
- Biased samples. The best-known industry reports are built from whatever data their authors can get. Verizon's DBIR draws on incidents contributed by its partners, which change from year to year; IBM's Cost of a Data Breach report studies organizations that had a breach and agreed to be interviewed; Mandiant's M-Trends describes the intrusions Mandiant was hired to investigate, which skew toward serious cases. Each is valuable, and each describes its own sample, not "all organizations."18234
- Means and medians. Breach costs are heavily skewed by a few very large events. IBM reports averages; a median would be lower. Use the statistic that matches the question.
- Spending ratios. Security spending as a share of IT budget or revenue is a common board benchmark, but it measures inputs. A company spending more than its peers may be catching up from years of neglect, or buying tools it does not use. Lesson 2 covers budget benchmarks and their sources.
- Vendor-sponsored surveys. Many widely quoted statistics come from surveys run by companies that sell the solution to the problem the survey finds. Check who paid, how many people answered, and how they were chosen.
- Maturity scores from different assessors. A "3.1 on the CSF" from one consulting firm and a "3.1" from another are not the same measurement.
- Comparing yourself to the average. Being average in a population that is regularly breached is not a goal. The most useful comparison is usually with your own trend and your own stated tolerance.
Benchmarks are most useful for a few hard, well-defined numbers (for example, the share of breaches starting with exploited vulnerabilities, or the federal remediation clocks in BOD 26-04) that help set targets, and for prompting questions ("peers report their boards practice an incident response test; have we?").

Public sector metrics and the Idaho angle
Public agencies report to legislatures, commissions, elected boards and the public rather than to shareholders, and their metrics often become public records. Federal agencies use the FISMA maturity levels described above, and inspector general FISMA reports are published on Oversight.gov.16 Many states and large local governments use the NIST Cybersecurity Framework or the CIS Critical Security Controls as their measuring stick.
Idaho built its executive branch program on both. Executive Order 2017-02, signed by Gov. C.L. "Butch" Otter on Jan. 16, 2017, adopted the findings of the Idaho Cybersecurity Cabinet Taskforce: state agencies were to adopt the NIST Cybersecurity Framework by June 30, 2017, implement the first five CIS Critical Security Controls by June 30, 2018, conduct annual penetration tests and vulnerability scans, and give state employees mandatory annual cybersecurity training.39 Those dated commitments are themselves measurable: completion of the CIS controls, test frequency and training completion rates. In 2018 the Legislature created the Office of Information Technology Services, whose administrator oversees statewide IT and "cybersecurity policies" (Idaho Code 67-827), and the Idaho Technology Authority, under Idaho Code 67-831 to 67-833, sets statewide IT policies and standards.4041 This lesson could not find a published statewide Idaho security metrics dashboard as of Nov. 15, 2026. Counties, cities, school districts and public hospital districts in Idaho set their own practices, often through their insurers and risk pools; lesson 9 covers what insurers ask for.
For any public body, the same principles apply as for a corporate board: a few metrics tied to real risks, a tolerance set by the governing body, trends, and minutes that show the questions. One difference matters. Detailed security metrics (which systems are unpatched, which controls are missing) can help attackers, and Idaho's Public Records Act exempts records about cybersecurity devices, programs and systems and certain critical infrastructure vulnerability assessments from disclosure.42 A public body can publish the summary (trend, tolerance, whether it was met) while protecting the technical detail.
Sample: Board Security Report template
Sample only. Adapt it to your organization's risks, systems and laws, have qualified people review it, and do not treat it as a substitute for a risk assessment.
Follows: NIST SP 800-55 Vol. 1 and Vol. 2 (December 2024); NIST Cybersecurity Framework 2.0, Govern function, GV.RM and GV.OV (Feb. 26, 2024); 16 CFR 314.4(i); 23 NYCRR 500.4; 12 CFR Part 30, Appendix B, section III.F; Regulation S-K Item 106(c); NACD and ISA, Director's Handbook on Cyber-Risk Oversight, fifth edition (2026), principle on measurement and reporting.
[Organization name] Cybersecurity Report to the [Board of Directors / Risk Committee / Audit Committee / Commission]
Reporting period: [quarter and dates]. Prepared by: [CISO name and title]. Reviewed by: [executive sponsor]; metrics recomputed by [internal audit, on a sample basis, date]. Classification: [Confidential; board use only].
1. Summary (no more than five sentences). [Overall assessment in plain English. Whether any board-approved tolerance was breached this period, for how long, and what was done. The one thing the board most needs to know.]
2. Risk indicators against appetite. [Six to ten metrics. For each: name and catalog number; question it answers; current value; target; tolerance approved by the board on [date]; values for the last four quarters; status (within, approaching, over tolerance), with the numeric threshold for each status; owner; one-line explanation.]
| Indicator | Now | Target | Tolerance | Last 4 quarters | Status | Owner | Comment |
|---|---|---|---|---|---|---|---|
| [Exposed known exploited vulnerabilities past internal deadline] | [ ] | [0] | [ ] | [ ] | [ ] | [ ] | [ ] |
| [Privileged accounts with phishing-resistant MFA, percent] | [ ] | [100%] | [ ] | [ ] | [ ] | [ ] | [ ] |
| [Tier 1 systems restore-tested in last 12 months] | [ ] | [all] | [ ] | [ ] | [ ] | [ ] | [ ] |
| [Median hours from first alert to containment, severity 2 and above; percent detected internally] | [ ] | [ ] | [ ] | [ ] | [ ] | [ ] | [ ] |
| [Critical vendors with current assessment and contract security terms] | [ ] | [100%] | [ ] | [ ] | [ ] | [ ] | [ ] |
| [High-risk policy exceptions and risk acceptances older than 90 days] | [ ] | [0] | [ ] | [ ] | [ ] | [ ] | [ ] |
| [Phishing: percent of simulations reported within one hour; real reports per month] | [ ] | [ ] | [ ] | [ ] | [ ] | [ ] | [ ] |
| [End-of-support internet-facing devices] | [ ] | [0] | [ ] | [ ] | [ ] | [ ] | [ ] |
3. Definition changes. [Any change to a metric's formula, scope or data source since the last report; whether earlier quarters were restated.]
4. Incidents and events. [Incidents at or above severity [level], with date detected, date contained, systems and data affected, whether the materiality process was triggered and its outcome, and notices made to regulators or individuals. Significant incidents at critical vendors or peers and what they changed. Regulatory examinations, letters or inquiries.]
5. Program plan. [Top five initiatives from the [Target Profile / roadmap]: description, budget, original and current completion dates, status, reason for any slip.]
6. Assurance. [Results of internal audit work, external assessments (SOC reports, certifications, penetration tests, regulatory exams) this period; count and age of open high-risk findings; overdue items.]
7. Risk acceptances and exceptions requiring board attention. [Any risk above management's acceptance authority under the [risk appetite statement / policy], with compensating controls and expiry date.]
8. Decisions requested. [Each decision, the options, the recommendation, and the consequence of no decision.]
9. CISO's independent view. [Any matter the CISO believes the board should know on which management's view differs, or a statement that there is none.]
Appendices. [Metric catalog entries for every indicator shown; threat briefing; detailed project status; glossary.]
Pictures, Numbers and Infographics
The key numbers in this lesson, each with its source.
| Number | What it is | Source |
|---|---|---|
| Dec. 4, 2024 | NIST publishes SP 800-55 Vol. 1 and Vol. 2, replacing the July 2008 Rev. 1 | NIST CSRC12 |
| 4 types | Implementation, effectiveness, efficiency and impact measures | SP 800-55 Vol. 11 |
| 5 steps | Measurement program workflow, from evaluating the program to applying corrective actions | SP 800-55 Vol. 22 |
| 4 Tiers | CSF 2.0: Partial, Risk Informed, Repeatable, Adaptive | NIST CSWP 29, Feb. 26, 202415 |
| Level 4 | "Managed and Measurable," the FISMA maturity level OMB treats as effective | FY 2025 IG FISMA Reporting Metrics v2.016 |
| 1,781; 361 | Entries in CISA's KEV catalog; entries known to be used in ransomware campaigns | KEV version 2026.11.133 |
| 3, 14 or 60 days | Federal remediation clocks under BOD 26-04, which replaced BOD 22-01 on June 10, 2026 | CISA BOD 26-0421 |
| 20 percent; 54 percent; 32 days | Breaches starting with vulnerability exploitation (2025 DBIR); edge device flaws fully fixed; median days to fix | Verizon 2025 DBIR18 |
| 32 percent | Intrusions starting with an exploit in Mandiant's 2025 cases | M-Trends 20264 |
| 14 days (from 11) | Global median dwell time in Mandiant's 2025 investigations | M-Trends 20264 |
| 52 percent (from 43) | Share of intrusions organizations detected themselves, 2025 | M-Trends 20264 |
| 241 days; $4.44 million | Mean time to identify and contain a breach; global average breach cost | IBM Cost of a Data Breach 202523 |
| 247 days; $4.99 million | Same measures in IBM's 2026 report (secondary summary) | Baker Donelson summary of IBM 202624 |
| 21 percent vs. 5 percent | Phishing simulation report rate with training in prior 30 days vs. base rate | Verizon 2025 DBIR28 |
| 73.13 percent | Public company directors agreeing their own cyber understanding is strong enough for oversight | NACD 2025 survey5 |
| 32.72 percent | Boards that took part in a test of the response plan in the past year | NACD 2025 survey37 |
| 29 percent | Directors rating CISO cyber updates "very effective" | IANS, Artico Search and The CAP Group, 202638 |
| $80 million | OCC civil money penalty against Capital One, Aug. 2020 | OCC consent order 2020-03611 |
| $2,125,000 | SEC penalty against R.R. Donnelley for cyber-related controls failures, June 18, 2024 | SEC press release 2024-7514 |
| $487,616; $3 million | SEC penalties: First American (2021) and Blackbaud (2023) | SEC press releases1213 |
Common mistakes
Each of these failures is documented in a public enforcement order, court opinion or government report. Several are also covered from the incident response angle in Detection and Incident Response; here the focus is on what the measurement and reporting system should have caught.
1. A board that receives the warnings but does not hold management to them
After the 2019 Capital One breach, in which an outsider took customer data from the bank's cloud environment, the Office of the Comptroller of the Currency assessed an $80 million civil money penalty in an order signed Aug. 5, 2020. The OCC found that the bank "failed to establish effective risk assessment processes" before moving significant operations to the public cloud, that internal audit "failed to identify numerous control weaknesses and gaps in the cloud operating environment," and that when internal audit did raise concerns, "the Board failed to take effective actions to hold management accountable."11 Fix: every open audit finding and breached tolerance goes on the board report with an owner and a date, and the committee asks about the oldest ones by name.
2. Alerts that never reach anyone
The SEC fined R.R. Donnelley & Sons $2,125,000 on June 18, 2024 over a 2021 ransomware intrusion. According to the SEC's order, the company's intrusion detection systems began issuing alerts on Nov. 29, 2021; its outside managed security provider escalated three of them to company staff, and in November and December 2021 also "reviewed, but did not escalate to RRD, at least 20 other alerts related to the same activity, including alerts regarding the same malware being installed or executed on multiple other computers across the network." The company's own staff assigned to escalated alerts had "significant other responsibilities," and the company did not begin actively responding until Dec. 23, 2021, after a company with shared access to its network alerted its CISO.1443 Two commissioners, Hester Peirce and Mark Uyeda, dissented from the legal theory, arguing that the accounting controls provision the SEC used does not reach computer systems; their objection was to the law, not to the facts about the alerts.44 Fix: measure how many alerts from service providers are escalated, how many are reviewed within the agreed time, and how many incidents were found some other way. The Senate's 2014 staff report on the Target breach describes the same pattern a decade earlier.45
3. The security staff know; the executives speaking in public do not
In 2021 the SEC fined First American Financial $487,616 because its information security staff had identified the vulnerability that exposed customer document images months before the company's public statements about it, but had not fixed it, and the executives who made the statements were never told.12 In 2023 Blackbaud paid $3 million after it told customers a ransomware attacker had not taken donor bank account information or Social Security numbers, when its technology and customer relations staff had learned within days that the attacker had; they did not tell the senior managers responsible for disclosure.13 Fix: a reporting rule that moves any vulnerability or incident affecting regulated data to the disclosure committee within a set time, and a metric for it (time from discovery to disclosure committee notice).
4. Measuring a tool that has gone blind
At Equifax, the Government Accountability Office found, a device meant to inspect encrypted network traffic was misconfigured because of "an expired digital certificate" that "had expired about 10 months before the breach occurred," and the attack "lasted for about 76 days before it was discovered."46 Every dashboard that relied on that device's alerts was quietly reporting on a sensor that saw nothing. Fix: measure the health of security tools themselves (sensors reporting in, log sources silent for more than 24 hours, certificates near expiry) and put the count on the executive report.
5. Public statements that outrun the internal picture
In its 2023 suit against SolarWinds and its CISO, the SEC alleged that internal presentations described serious weaknesses while the company's public security statement described good practices. A federal judge dismissed most of the claims in July 2024, leaving only claims about the public security statement, and the SEC dropped the rest of the case on Nov. 20, 2025.4748 Whatever one concludes about the case, the lesson for reporting is plain: internal metrics and external statements should be reconciled before anything is published, and the people who write the 10-K's Item 1C should see the same dashboard the committee sees.
6. Reporting that simply stops
The Delaware Court of Chancery's 2022 opinion in the SolarWinds derivative case recited that the board committee responsible for cyber received one briefing in early 2019 and that the full board held no meetings or discussions on cybersecurity from the company's October 2018 IPO until the December 2020 attack; the court dismissed the claims but called the reporting system "subpar."32 Fix: put cyber on the committee calendar for every regular meeting and on the full board's calendar at least once a year, and track attendance and follow-ups like any other governance metric.
7. Too many numbers, no story
This one rarely reaches an enforcement order because it fails quietly: forty slides of activity metrics, color codes without thresholds, and no statement of what the board should conclude. NIST's warning that "poorly selected quantitative metrics can undermine the overall quality of reporting and erode confidence in the work product" applies directly.1 Fix: one page on top, a catalog behind it, and the five questions in the board reporting section answered every time.
Questions people ask
How many metrics should the board see?
Usually six to ten, chosen from the organization's top risks, plus a short incident summary and the plan. Executives may see thirty; operational teams may track hundreds. NIST's advice for new programs ("less is often more") applies most strongly at the top.1 If a director cannot remember what the numbers were a week later, there were too many.
Should we report cyber risk in dollars?
Where you can do it honestly, yes, as ranges with stated assumptions. Dollar ranges let directors compare cyber with other risks and judge whether a project is worth funding. Where data are thin, a well-defined operational KRI with a tolerance is better than an invented dollar figure. NIST's Volume 2 expects programs to start with implementation measures and move toward business impact as they mature.2 The methods are in Risk Management in Plain Terms.
Who sets the targets and tolerances?
Management proposes them, tied to the risk appetite statement, and the board or its committee approves them. CSF 2.0 calls for "risk appetite and risk tolerance statements" that are "established, communicated, and maintained" (GV.RM-02).15 Approval matters: a tolerance the board approved turns a breach into a governance event that must be reported, rather than a number management can quietly explain away.
Should internal audit check the metrics?
Yes, at least on a rotating sample. A metric that has never been independently recomputed is an assertion. The IIA's Cybersecurity Topical Requirement, effective Feb. 5, 2026, expects internal audit to assess cyber governance, which includes the reporting to the board.30 See lesson 8.
What should change in reporting after a major incident?
The board will want to know why the metrics did not warn them. Usually one of three things happened: the risk was not measured, it was measured but excluded from the denominator, or it was measured and reported but nobody acted. The after-action review should say which, and the metric catalog should change accordingly. The CSF expects improvements to come from incidents and exercises (ID.IM-02 and ID.IM-03).15
Should we share metrics with customers, insurers or regulators?
Selectively. Insurers ask for many of the same numbers at renewal (MFA coverage, backup testing, patch timelines), and consistency between what the board sees and what the insurer is told matters; misstatements on insurance applications have led to coverage disputes, as lesson 9 explains. Regulators may request board materials during an examination. Write every board report as though a regulator, an insurer or a court might read it later.
Does a small public body need all of this?
No. A county commission or a school board can do well with four or five numbers (MFA coverage, patching of internet-facing systems, a tested backup, training and reporting rates, and incidents) reported twice a year with a short narrative. Module 73's board reporting lesson shows that scale.
Hard questions
Should public companies have to publish security metrics?
For publication: investors price risk, and Item 1C disclosures say who is briefed and how often but nothing about whether the program works. A few standardized metrics (such as MFA coverage for privileged accounts or the share of critical systems restore-tested) would let investors compare companies, much as financial ratios do, and would make board oversight claims testable. Against: published metrics could help attackers pick targets, would invite gaming once they became public scores, and would be hard to define consistently across industries; the SEC itself dropped some proposed governance disclosures from its final 2023 rule, and in 2026 it opened a review of Regulation S-K in which trade groups argued for fewer, not more, cyber disclosures.3549 What the evidence shows: no U.S. regulator requires published security metrics, and the 10-Ks reviewed for this lesson contain none. The practical middle ground is what Item 106 already does: disclose the process, and let enforcement test whether the process is real.
Quantified dollar risk: better decisions or false precision?
For quantification: boards decide in dollars; a risk stated as a probable loss range can be compared with an insurance premium, a project cost or a market risk, and NIST's December 2025 guidance on integrating cybersecurity with enterprise risk management says "Quantitative methods are preferred" where data allow.50 Against: loss data for rare, severe cyber events are thin, models depend heavily on assumptions, and a precise-looking number can carry more authority than it deserves. What the evidence shows: both sides are right in different places. Quantification works best for frequent, well-understood events (fraud losses, phishing-driven account takeovers) and for comparing options, and least well for one-in-twenty-year catastrophes. Reporting ranges, showing assumptions and testing estimates against actual losses over time keeps it honest. Risk Management in Plain Terms covers the methods.
Should executive pay be tied to security metrics?
For: what gets paid gets done; tying part of executive bonuses to a few security outcomes signals priority and gives operations leaders, not just the CISO, a reason to care. Against: pay-linked metrics are the most likely to be gamed (by narrowing scope, reclassifying findings or under-reporting incidents), and they can punish honest reporting of bad news. What the evidence shows: directors are lukewarm. In NACD's 2025 survey, "alignment of compensation incentives with corporate cybersecurity objectives" was the improvement area most often rated "not at all important" (30.57 percent), and only 19.75 percent rated it very or extremely important.6 If pay is tied, it is safer to tie it to delivery of funded plan milestones and to independently verified metrics than to incident counts.
Is boards' confidence in their cyber oversight justified?
Yes, mostly: boards now hear about cyber regularly, have committee charters that name it, and disclose the arrangements publicly; directors say their understanding has improved, and since the 2023 SEC rules every public company must describe its oversight arrangement in its 10-K. Not yet: about a third of boards in the NACD survey had practiced an incident response test in the past year, directors in the 2026 IANS report rated reporting on threat impact and business risk the weakest, and the enforcement cases show reporting systems that looked fine on paper and failed in practice.3738 What the evidence shows: self-reported confidence is not a measure of oversight quality. The better tests are observable: whether tolerances exist and were acted on when breached, whether the board has rehearsed a material incident decision, and whether internal audit has checked the numbers.
For reporters and advocates
Security metrics themselves are rarely public, but a good deal about how organizations measure and report is.
- 10-K Item 1C. Every SEC-registered company's annual report describes which committee oversees cyber, how often it is briefed and by whom, and the expertise of the people responsible. Use EDGAR full-text search for "Item 1C" plus a company name, and compare a company's statements year to year: a change in committee, frequency or CISO reporting line is often a sign of change inside.517
- Form 8-K Item 1.05 and later 10-K statements. When a company discloses a material incident, compare what it said about board oversight in its prior 10-K with what the incident revealed. 108's governance lesson explains the filing rules.
- Enforcement orders. SEC orders (First American, Blackbaud, R.R. Donnelley), OCC orders (Capital One) and FTC orders describe, in detail, what internal reporting failed. They are the best public record of how measurement and escalation break down.12131411
- Inspector general FISMA reports. Federal agency IGs publish annual FISMA evaluations on Oversight.gov, with maturity ratings by CSF function and open recommendations. They are a ready-made comparison across agencies and years.16
- Court records. Derivative suits after breaches (on PACER, CourtListener and state court sites, such as the Delaware Court of Chancery) often quote board minutes and internal reports obtained through books-and-records demands.32
- Idaho public records. Under the Idaho Public Records Act (Idaho Code Title 74, Chapter 1), you can ask a state agency, county, city, school district or public hospital district for the dates and agendas of governing-body cyber briefings, the board-approved security policy, any approved risk tolerance or metrics, training completion rates (required for state employees under Executive Order 2017-02), and the summary results of audits. Expect technical detail to be withheld under the cybersecurity exemptions in Idaho Code 74-105; ask for the summary and the trend instead.524239
Questions worth asking a company, agency or hospital: Which committee hears about cyber, and how often? Does the board approve tolerances for any security metrics, and were any breached last year? Has internal audit checked the numbers the board sees? When did the board last rehearse a major incident? Who decides whether an incident is material, and how fast does that person hear about it? Does the CISO ever meet the committee without other executives present? And for Boise's public companies, whose 10-Ks describe quarterly briefings: what do those briefings contain?
Where to go next
- NIST SP 800-55 Vol. 1 and Vol. 2: Free federal guides to choosing security measures and running a measurement program. For CISOs, risk managers and internal auditors. Read Vol. 1 section 3.3 for the four measure types and Vol. 2 section 3 for the workflow before building a metric catalog.
- NIST Cybersecurity Framework 2.0 and quick-start guides: Free. Use the Organizational Profile steps and the Govern outcomes (GV.RM, GV.OV) to set a Target Profile, tolerances and a gap plan the board can track.
- CISA Known Exploited Vulnerabilities Catalog: Free list of flaws attackers are using, with a downloadable feed. For IT and security teams; the basis of the most useful patching KRI.
- FY 2025 IG FISMA Reporting Metrics: Free. The federal maturity scale (Ad Hoc to Optimized) by CSF function. Useful to public agencies and to anyone wanting a ready-made definition of 'managed and measurable.'
- SEC EDGAR full text search: Free. Search 'Item 1C' with a company name to read how its board is briefed on cyber, and compare peers and years. For directors, investors, reporters and advocates.
- NACD Board Practices and Oversight Survey data tables: Free data tables from NACD's annual director survey; some analysis is for members. Useful for comparing your board's practices with peers, keeping in mind these are self-reports.
- Oversight.gov: Free. Federal inspector general reports, including annual FISMA evaluations that show how independent auditors rate agency measurement and oversight.
Still being checked (5 items)
These points could not be fully confirmed against a primary source when this lesson was written and fact checked in November 2026. The text above states each one as uncertain.
- Verizon 2026 DBIR remediation figures (26 percent of known exploited vulnerabilities fully fixed, median 43 days) come from a secondary summary by watchTowr and were not checked against the full report.
- IBM Cost of a Data Breach 2026 figures ($4.99 million, $11.5 million U.S., 247 days) come from a law firm summary; the full IBM report was not read.
- The IANS, Artico Search and CAP Group 2026 report's sample size and survey dates were not stated in the published summary.
- Several citations (Verizon 2025 DBIR, BOD 26-02 and 26-04, NYDFS 500.4, the Equifax GAO report, the Target Senate report, First American, Blackbaud, SolarWinds and Idaho sources) were verified for module 108 on Nov. 13 to 14, 2026 and reused here without a fresh full reading; the GAO site refused an automated download on Nov. 15, 2026.
- This lesson could not find a published statewide Idaho security metrics dashboard; a more thorough search of Idaho ITS and Legislative Services Office publications was not completed because the web search budget for the build ran out.
Last verified November 15, 2026. General education, not legal, compliance, audit or other professional advice; rule versions and dates are stated in the text, and the sources used are listed in the Notes and Sources below. Check the regulator's current text before relying on any point.
Notes
- Katherine Schroeder, Hung Trinh and Victoria Pillitteri, Measurement Guide for Information Security: Volume 1, Identifying and Selecting Measures, NIST SP 800-55 Vol. 1 (Dec. 4, 2024; supersedes SP 800-55 Rev. 1, July 16, 2008), sections 1.4 (terminology), 2.4 (metrics), 3.3 (types of measures) and 4. Local copy saved in the lesson's working folder (read Nov. 15, 2026). Read it online. ↩
- Katherine Schroeder, Hung Trinh and Victoria Pillitteri, Measurement Guide for Information Security: Volume 2, Developing an Information Security Measurement Program, NIST SP 800-55 Vol. 2 (Dec. 4, 2024), sections 2.4 (roles) and 3 (workflow: evaluation and definition, identification and prioritization, data collection and analysis, corrective actions) (read Nov. 15, 2026). Read it online. ↩
- Cybersecurity and Infrastructure Security Agency, Known Exploited Vulnerabilities Catalog, JSON feed, catalog version 2026.11.13 (released Nov. 13, 2026): 1,781 entries; 361 flagged "Known" for ransomware campaign use; additions by year 2021: 311, 2022: 555, 2023: 187, 2024: 186, 2025: 245, 2026 to date: 297, computed for this lesson from the feed (read Nov. 15, 2026). Read it online. ↩
- Google Cloud (Mandiant), "M-Trends 2026: Data, Insights, and Strategies From the Frontlines," March 23, 2026, on investigations conducted in 2025: exploits 32 percent of intrusions (most common vector for the sixth year); global median dwell time 14 days, up from 11; 52 percent of intrusions first detected internally, up from 43 percent in 2024 (read Nov. 15, 2026). Read it online. ↩
- National Association of Corporate Directors, 2025 Public Company Board Practices and Oversight Survey, data table "Board Perspectives on Cybersecurity Oversight" (published July 28, 2025; 158 to 160 respondents per statement) (read Nov. 15, 2026). Read it online. ↩
- National Association of Corporate Directors, 2025 Public Company Board Practices and Oversight Survey, data table "Areas for Improvement in Cyber-Risk Oversight" (published July 28, 2025; 154 to 161 respondents per item) (read Nov. 15, 2026). Read it online. ↩
- 17 CFR 229.106 (Regulation S-K Item 106, Cybersecurity), paragraphs (b) and (c) and Instruction 2, eCFR current as of Nov. 2026 (read Nov. 15, 2026). Read it online. ↩
- Micron Technology, Inc., Annual Report on Form 10-K for the fiscal year ended Sept. 3, 2026, filed Oct. 9, 2026, Item 1C, Cybersecurity, SEC EDGAR (read Nov. 15, 2026). Read it online. ↩
- IDACORP, Inc. and Idaho Power Company, Annual Report on Form 10-K for the year ended Dec. 31, 2025, filed Feb. 19, 2026, Item 1C, Cybersecurity, SEC EDGAR (read Nov. 15, 2026). Read it online. ↩
- Albertsons Companies, Inc., Annual Report on Form 10-K for the fiscal year ended Feb. 28, 2026, filed April 27, 2026, Item 1C, Cybersecurity, SEC EDGAR (read Nov. 15, 2026). Read it online. ↩
- Office of the Comptroller of the Currency, In the Matter of Capital One, N.A., and Capital One Bank (USA), N.A., Consent Order for the Assessment of a Civil Money Penalty, Order No. 2020-036 (signed Aug. 5, 2020), Articles II and III ($80,000,000), copy published by Courthouse News (read Nov. 15, 2026). Read it online. ↩
- U.S. Securities and Exchange Commission, "SEC Charges Issuer With Cybersecurity Disclosure Controls Failures," Press Release 2021-102 (June 15, 2021), First American Financial Corporation, $487,616 (read Nov. 13, 2026, for module 108). Read it online. ↩
- U.S. Securities and Exchange Commission, "SEC Charges Software Company Blackbaud Inc. for Misleading Disclosures About Ransomware Attack That Impacted Charitable Donors," Press Release 2023-48 (March 9, 2023), $3 million (read Nov. 13, 2026, for module 108). Read it online. ↩
- U.S. Securities and Exchange Commission, "SEC Charges R.R. Donnelley and Sons Co. with Cybersecurity-Related Controls Violations," Press Release 2024-75 (June 18, 2024), civil penalty of $2,125,000; order in Release No. 34-100365 (read Nov. 15, 2026). Read it online. ↩
- National Institute of Standards and Technology, The NIST Cybersecurity Framework (CSF) 2.0, NIST CSWP 29 (Feb. 26, 2024), section 3.1 (Organizational Profiles), section 3.2 (Tiers), Appendix A categories GV.RM, GV.OV and ID.IM. Local copy saved (read Nov. 15, 2026). Read it online. ↩
- Office of Management and Budget, CIGIE and CISA, FY 2025 Inspector General Federal Information Security Modernization Act of 2014 (FISMA) Reporting Metrics, Version 2.0 (April 3, 2025): five maturity levels, Level 4 as effective, domains mapped to CSF 2.0 functions (read Nov. 15, 2026). Read it online. ↩
- Brown and Company CPAs, Independent Audit of the Council of the Inspectors General on Integrity and Efficiency Compliance with the Federal Information Security Modernization Act of 2014, Fiscal Year 2026 (July 7, 2026), stating that the OMB FY 2025 IG FISMA Reporting Metrics remained in effect for FY 2026 (read Nov. 15, 2026). Read it online. ↩
- Verizon Business, 2025 Data Breach Investigations Report (released April 23, 2025; data Nov. 1, 2023 to Oct. 31, 2024): exploitation of vulnerabilities as the first step in 20 percent of breaches; third-party involvement up from 15 to 30 percent; about 54 percent of known edge device vulnerabilities fully remediated, median 32 days, as quoted in BankInfoSecurity, "Verizon Reports Surge in Breaches Tied to Edge Devices" (April 2025) (read Nov. 13, 2026, for module 108). Read it online. ↩
- Verizon Business, 2026 Data Breach Investigations Report, report page and summary statistics (page revised May 19, 2026; data Nov. 1, 2024 to Oct. 31, 2025): 31 percent of breaches began with exploitation of a software vulnerability (read Nov. 13, 2026, for module 108). Read it online. ↩
- watchTowr, "Verizon DBIR 2026: Vulnerability Exploitation Is Now #1 Way Breaches Start" (May 20, 2026), summarizing the 2026 DBIR: 26 percent of known exploited vulnerabilities fully remediated (down from 38 percent); median 43 days to remediate. Secondary summary, not checked against the full report (read Nov. 13, 2026, for module 108). Read it online. ↩
- Cybersecurity and Infrastructure Security Agency, Binding Operational Directive 26-04, "Prioritizing Security Updates Based on Risk" (June 10, 2026), with Implementation Guidance; revokes BOD 19-02 and BOD 22-01 (Nov. 3, 2021); remediation timelines in Phase III within 180 days (read Nov. 13, 2026, for module 108). Read it online. ↩
- 16 CFR 314.4(c)(5) (multifactor authentication), (d)(2) (continuous monitoring or annual penetration testing and vulnerability assessments at least every six months) and (i) (written report to the board "regularly and at least annually"), FTC Standards for Safeguarding Customer Information, eCFR current as of Nov. 2026 (read Nov. 15, 2026). Read it online. ↩
- IBM, "IBM Report: 13% Of Organizations Reported Breaches Of AI Models Or Applications, 97% Of Which Reported Lacking Proper AI Access Controls," press release (July 30, 2025), on the Cost of a Data Breach Report 2025 by the Ponemon Institute: global average $4.44 million; U.S. average $10.22 million; mean time to identify and contain 241 days; about $900,000 lower costs when the organization's own team found the breach (read Nov. 15, 2026). Read it online. ↩
- Baker Donelson, "Ten Takeaways from IBM's 2026 Cost of a Data Breach Report" (2026): global average $4.99 million; U.S. average $11.5 million; mean time to identify and contain 247 days; 602 breaches from March 2025 to February 2026. Secondary summary; the full IBM report was not read (read Nov. 15, 2026). Read it online. ↩
- Daniele Lain, Kari Kostiainen and Srdjan Capkun, "Phishing in Organizations: Findings from a Large-Scale and Long-Term Study," 2022 IEEE Symposium on Security and Privacy, pp. 842 to 859 (preprint arXiv:2112.07498) (read Nov. 13, 2026, for module 108). Read it online. ↩
- Grant Ho, Ariana Mirian, Elisa Luo and colleagues, "Understanding the Efficacy of Phishing Training in Practice," 2025 IEEE Symposium on Security and Privacy (May 2025) (read Nov. 13, 2026, for module 108). Read it online. ↩
- National Institute of Standards and Technology, "The Phish Scale: NIST-Developed Method Helps IT Staff See Why Users Click on Fraudulent Emails" (Sept. 2020), on Michelle Steves, Kristen Greene and Mary Theofanos, "Categorizing human phishing difficulty: a Phish Scale," Journal of Cybersecurity 6, no. 1 (2020) (read Nov. 13, 2026, for module 108). Read it online. ↩
- Verizon Business, 2025 Data Breach Investigations Report, pp. 47 to 49 (phishing simulation data: report rate about 21 percent for employees trained in the prior 30 days versus a base rate of about 5 percent) (read Nov. 13, 2026, for module 108). Read it online. ↩
- Cybersecurity and Infrastructure Security Agency, Binding Operational Directive 26-02, "Mitigating Risk From End-of-Support Edge Devices" (Feb. 5, 2026) (read Nov. 13, 2026, for module 108). Read it online. ↩
- EisnerAmper, "Cybersecurity Topical Requirement: What You Need to Know" (2025), describing the IIA Cybersecurity Topical Requirement issued February 2025 and effective Feb. 5, 2026 under the IIA Global Internal Audit Standards (read Nov. 13, 2026, for module 108). Read it online. ↩
- National Association of Corporate Directors, "New Guide for Corporate Boards Addresses the Rising Stakes for Cyber-Risk Oversight," press release (April 16, 2026), on the NACD and Internet Security Alliance Director's Handbook on Cyber-Risk Oversight, fifth edition (read Nov. 13, 2026, for module 108). Read it online. ↩
- Construction Industry Laborers Pension Fund v. Bingle, C.A. No. 2021-0940-SG (Del. Ch. Sept. 6, 2022) (Glasscock, V.C.), memorandum opinion (SolarWinds derivative litigation), affirmed (Del. May 17, 2023) (read Nov. 13, 2026, for module 108). Read it online. ↩
- New York Department of Financial Services, 23 NYCRR Part 500, Cybersecurity Requirements for Financial Services Companies, as amended effective Nov. 1, 2023, section 500.4 (read Nov. 13, 2026, for module 108). Read it online. ↩
- 12 CFR Part 30, Appendix B, Interagency Guidelines Establishing Information Security Standards, sections III.A and III.F, eCFR (read Nov. 13, 2026, for module 108). Read it online. ↩
- U.S. Securities and Exchange Commission, "Cybersecurity Risk Management, Strategy, Governance, and Incident Disclosure," Release Nos. 33-11216 and 34-97989, 88 Fed. Reg. 51896 (Aug. 4, 2023), effective Sept. 5, 2023; Item 106 disclosures required for fiscal years ending on or after Dec. 15, 2023 (read Nov. 13, 2026, for module 108). Read it online. ↩
- JPMorgan Chase and Co., Annual Report on Form 10-K for the year ended Dec. 31, 2025, filed Feb. 13, 2026, Item 1C (cross-reference to the Operational Risk Management section of management's discussion and analysis, pp. 146 to 149), SEC EDGAR (read Nov. 15, 2026). Read it online. ↩
- National Association of Corporate Directors, 2025 Public Company Board Practices and Oversight Survey, data table "Cyber-Risk Oversight Practices Conducted in the Past Year" (published July 28, 2025; 162 respondents) (read Nov. 15, 2026). Read it online. ↩
- IANS Research, "Boards Give CISO Cybersecurity Reporting a Mixed Grade" (March 24, 2026), on the 2026 CISO-Board Engagement Report by IANS Research, Artico Search and The CAP Group; sample size not stated in the summary (read Nov. 15, 2026). Read it online. ↩
- Idaho Executive Order 2017-02, "Findings of the Idaho Cybersecurity Cabinet Taskforce," signed by Gov. C.L. "Butch" Otter (Jan. 16, 2017) (read Nov. 13, 2026, for module 108). Read it online. ↩
- Idaho Office of Information Technology Services, "IT Statutes and Executive Orders" (Idaho Code 67-827 and 67-831 to 67-833; Executive Orders 2015-07 and 2017-02) (read Nov. 13, 2026, for module 108). Read it online. ↩
- Idaho Code 67-827, Coordination of policy and programs, Information Technology Services and Cybersecurity (added 2018) (read Nov. 13, 2026, for module 108). Read it online. ↩
- Idaho Code 74-105, Records exempt from disclosure, subsections (4)(b) (critical infrastructure records, including vulnerability assessments) and (21) (cybersecurity devices, programs or systems) (read Nov. 13, 2026, for module 108). Read it online. ↩
- U.S. Securities and Exchange Commission, In the Matter of R.R. Donnelley and Sons Co., Order Instituting Cease-and-Desist Proceedings, Release No. 34-100365 (June 18, 2024), paragraphs 8 to 14 (alerts from Nov. 29, 2021; three alerts escalated; at least 20 other alerts not escalated; active response from Dec. 23, 2021) and Section IV ($2.125 million civil penalty) (read Nov. 16, 2026). Morrison Foerster's June 25, 2024 summary of the order is at https://mofo.com/resources/insights/240625-the-sec-s-controls-based-approach-to-cybersecurity. Read it online. ↩
- Commissioners Hester M. Peirce and Mark T. Uyeda, "Hey, look, there's a hoof cleaner! Statement on R.R. Donnelley and Sons, Co." (June 18, 2024) (read Nov. 15, 2026). Read it online. ↩
- U.S. Senate Committee on Commerce, Science, and Transportation, Majority Staff Report, A "Kill Chain" Analysis of the 2013 Target Data Breach (March 26, 2014) (read Nov. 13, 2026, for module 108). Read it online. ↩
- U.S. Government Accountability Office, Data Protection: Actions Taken by Equifax and Federal Agencies in Response to the 2017 Breach, GAO-18-559 (Aug. 30, 2018), pp. 10 to 14 (read Nov. 13, 2026, for module 108). Read it online. ↩
- Covington and Burling LLP, "SEC Voluntarily Dismisses SolarWinds Litigation," Inside Privacy (November 2025), summarizing Judge Paul A. Engelmayer's July 18, 2024 opinion granting in part the motion to dismiss and the November 2025 dismissal (read Nov. 13, 2026, for module 108). Read it online. ↩
- U.S. Securities and Exchange Commission, Litigation Release No. 26423, SEC v. SolarWinds Corp. and Timothy G. Brown, No. 1:23-cv-09518-PAE (S.D.N.Y.) (Nov. 20, 2025) (read Nov. 13, 2026, for module 108). Read it online. ↩
- "Statement by Chair Atkins on Reforming Regulation S-K," Harvard Law School Forum on Corporate Governance (Jan. 15, 2026), on the Jan. 13, 2026 request for comment (File No. CLL-15); see also SIFMA and other trade associations, "Reforming Regulation S-K's Cybersecurity Disclosures (Joint Trades)," comment letter, April 2026 (read Nov. 13, 2026, for module 108). Read it online. ↩
- Stephen Quinn and colleagues, Integrating Cybersecurity and Enterprise Risk Management (ERM), NIST IR 8286 Revision 1 (December 2025), section 3.3.1 (qualitative and quantitative analysis) (read Nov. 13, 2026, for module 108). Read it online. ↩
- U.S. Securities and Exchange Commission, EDGAR full text search (read Nov. 15, 2026). Read it online. ↩
- Idaho Code Title 74, Chapter 1, Public Records Act (read Nov. 13, 2026, for module 108). Read it online. ↩
Check yourself
1. In NIST SP 800-55 Vol. 1 (December 2024), what turns a measure into a metric?
SP 800-55 Vol. 1, section 1.4, defines metrics as measures and assessment results designed to track progress, facilitate decision-making and improve performance with respect to a set target.
2. Which of these is a key risk indicator (KRI) rather than an activity metric?
A KRI warns that exposure is growing past a tolerance. Blocked emails, scans run and tickets closed are activity counts; NIST SP 800-55 Vol. 1 says good metrics should illustrate a valid control or track a material risk.
3. What are the four CSF 2.0 Tiers?
NIST CSWP 29 (Feb. 26, 2024), section 3.2, names the Tiers Partial (1), Risk Informed (2), Repeatable (3) and Adaptive (4). The FISMA IG metrics use the five maturity levels in option C.
4. Under the FY 2025 IG FISMA Reporting Metrics, still in effect for FY 2026, what maturity level does OMB treat as an effective security program?
The FY 2025 IG FISMA Reporting Metrics v2.0 (April 3, 2025) state that achieving Level 4 (managed and measurable) or above represents an effective level of security.
5. What happened to CISA's BOD 22-01, the directive that set KEV due dates for federal agencies?
CISA BOD 26-04, Prioritizing Security Updates Based on Risk (June 10, 2026), revoked BOD 22-01 and BOD 19-02 and set clocks of 3, 14 or 60 days or fix on upgrade.
6. Verizon's 2025 DBIR found what about phishing simulation reporting?
Verizon 2025 DBIR, pp. 47 to 49: reporting rose to about 21 percent with recent training against a base rate of about 5 percent, while click rates changed far less.
7. Mandiant's M-Trends 2026 reported what global median dwell time for its 2025 investigations?
M-Trends 2026 (March 23, 2026): global median dwell time rose to 14 days from 11. The 241 days figure is IBM's 2025 mean time to identify and contain, a different measure.
8. What does Regulation S-K Item 106(c) require a public company's 10-K to describe?
17 CFR 229.106(c)(1) requires a description of board oversight, the responsible committee if any, and the processes by which the board or committee is informed. No metrics are required.
9. In the OCC's August 2020 Capital One consent order, what did the OCC find about the board?
OCC Order No. 2020-036 (Aug. 5, 2020), Article II, found the board failed to take effective actions to hold management accountable, alongside risk assessment and internal audit failures; penalty $80 million.
10. In NACD's 2025 public company survey, which oversight improvement area drew the highest share of 'extremely important' ratings?
NACD 2025 Public Company Board Practices and Oversight Survey (July 28, 2025): 12.66 percent rated acquiring metrics extremely important, the highest of the eight areas.
Terms in this lesson
- Measure
- In NIST SP 800-55 Vol. 1, a quantifiable and objective value that results from measurement, such as the number of servers missing a patch on a date.
- Metric
- A measure or assessment result designed to track progress, support decisions and improve performance with respect to a set target.
- Key performance indicator (KPI)
- A metric that shows how well a process or control performs, such as median days to fix known exploited flaws.
- Key risk indicator (KRI)
- A metric that warns when a specific risk is growing, compared against a tolerance the board or management approved.
- Key control indicator
- A metric that shows whether a single control is operating as designed, such as whether quarterly access reviews happened on time.
- Leading and lagging indicators
- Leading indicators measure conditions that make future incidents more or less likely; lagging indicators count incidents and losses that already happened.
- Implementation, effectiveness, efficiency and impact measures
- The four types of measures in NIST SP 800-55 Vol. 1: whether controls are in place, whether they work, how fast they act, and what security costs or saves the mission.
- Semi-quantitative assessment
- Scoring with bins or scales (such as 1 to 5 on a heat map) whose numbers do not keep their meaning outside that scale; NIST does not treat these as measurements.
- Current Profile and Target Profile
- CSF 2.0 Organizational Profiles describing the outcomes an organization achieves now and the outcomes it has chosen to achieve; the gap between them drives an action plan.
- Risk tolerance
- The acceptable level of variation around a risk objective; for a metric, the value that triggers escalation when crossed.
- Dwell time
- The time from the start of an intrusion to its detection; Mandiant reports the global median.
- Mean time to detect and mean time to respond (MTTD and MTTR)
- Average time from attacker activity to detection, and from detection to containment; useful only with a fixed definition of when each clock starts.
- Metric catalog
- The written definition of each metric: question, formula, data source, owner, target, tolerance, frequency, limits and change log.
- Item 1C
- The 10-K section where SEC registrants make the cybersecurity disclosures required by Regulation S-K Item 106, including board oversight.
- FISMA maturity levels
- The five levels inspectors general use to rate federal agency programs: Ad Hoc, Defined, Consistently Implemented, Managed and Measurable, Optimized.
Sources
- NIST SP 800-55 Vol. 1, Measurement Guide for Information Security: Identifying and Selecting Measures (2024-12-04) checked 2026-11
- NIST SP 800-55 Vol. 2, Measurement Guide for Information Security: Developing an Information Security Measurement Program (2024-12-04) checked 2026-11
- NIST Cybersecurity Framework 2.0 (CSWP 29) (2024-02-26) checked 2026-11
- 17 CFR 229.106, Regulation S-K Item 106, Cybersecurity (2023-08-04) checked 2026-11
- 16 CFR 314.4, FTC Safeguards Rule elements (2023-11-13) checked 2026-11
- CISA Binding Operational Directive 26-04, Prioritizing Security Updates Based on Risk (2026-06-10) checked 2026-11
- CISA Known Exploited Vulnerabilities Catalog (version 2026.11.13) (2026-11-13) checked 2026-11
- FY 2025 IG FISMA Reporting Metrics, Version 2.0 (2025-04-03) checked 2026-11
- OCC Consent Order 2020-036, Capital One (2020-08-05) checked 2026-11
- SEC Press Release 2024-75, R.R. Donnelley (2024-06-18) checked 2026-11
- Micron Technology Form 10-K, fiscal 2026, Item 1C (2026-10-09) checked 2026-11
- IDACORP and Idaho Power Form 10-K, 2025, Item 1C (2026-02-19) checked 2026-11
- Albertsons Companies Form 10-K, fiscal 2025, Item 1C (2026-04-27) checked 2026-11
- NACD 2025 Public Company Board Practices and Oversight Survey, cybersecurity data tables (2025-07-28) checked 2026-11
- Mandiant, M-Trends 2026 (2026-03-23) checked 2026-11